There are multiple reports circulating the Internet about current attacks exploiting an unpatched (0-day) vulnerability in Adobe products that is currently being actively exploited. It affects just about all recent versions of Acrobat Reader and Adobe Acrobat including v7, v8, and v9 and the issue appears to be a buffer overflow in the PDF Javascript processor. Javascript is allowed and enabled by default. The remediation/workaround is to disable the Javascript functionality in the Adobe products.
Additional reports are coming out that this exploit that was discovered may have been around as long ago as December 2008.
Adobe has released a bulletin and reports that they will have a patch released around March 11. I would recommend applying the workaround of disabling Javascript until the patch is released.
Remediation:
* Change Registry value "bEnableJS" to "0":
HKCU\Software\Adobe\Acrobat Reader\8.0\JSPrefs
HKCU\Software\Adobe\Adobe Reader\8.0\JSPrefs
February 21, 2009


February 12, 2009
APWG Phishing Education Landing Page
The Anti-Phishing Working Group (APWG) and Carnegie Mellon CyLab is asking that instead of disabling phishing sites you redirect the users to their Phishing Education Landing Page. I think this is a great way to educate your users about phishing. The more they know how phishing works the better they can protect themselves.
Here's how the program works: when a phishing site is shut down by officials (e.g. ISP, registrar, Web hosting company), we ask if the official would redirect the URL of the phishing site to an education landing page.
For more information about this program see http://education.apwg.org/r/how_to.html
January 27, 2009
Malicious links on President Obama's website
First it's fake Barack Obama websites spreading malware now the REAL BarackObama.com website is responsible for pushing the stuff. To be clear, it's not President Obama's people pushing it, it's a registered user of their site. Attackers are using one of the sites features called Community Blogs to place malicious links on the site.
 A recent attack that I looked at featured what appears to be a embedded video but when you click it you are redirected through a couple different sites finally to a site selling rogue/fraudulent security software and trojans.
Another unfortunate example of the dangers of Web 2.0 and while this technique of using blogs to spread malware is not new (Google dev site, Twitter, 2005, German Wikipedia) I expect to see it grow in popularity due to how effective it's proving. Oh joy.
More...
http://news.softpedia.com/news/Barack-Obama-039-s-Website-Used-to-Push-Malware-102977.shtml
http://securitylabs.websense.com/content/Blogs/3284.aspx
January 19, 2009
Fake US Presidential Inauguration and Obama Websites
Fake Barack Obama blogs and websites are being used to infect computers with a worm called Waledac. This worm appears to be from the same makers of the Storm worm according to several in the security community including Jose at Arbor Networks.
An example is hxxp://www.bestbaracksite.com/
(WARNING: Malicious site).

When visiting the site visitors see graphics and blog entries that look real and while they read the entries silently a drive-by install is placing malicious code on their system. All the links on the website point to a malicious EXE download as well. This site, by the way, is using "fast flux" DNS to avoid takedown and appears to be hosted on a botnet as some of the IPs appear to be home DSL/cable modem customers.
With the US presidential inauguration tomorrow I expect to continue to see a rise in this type of attack and recommend you check your web proxy logs for any domains with the following words in them:
barack
obama
presidential
inauguration
January 12, 2009
Guide to Protecting Yourself on Facebook
There is a great guide about how to protect yourself on Facebook written by a friend and security colleague of mine, Tom Eston. Tom has alot of experience researching social networking and has some really great tips that could be applied to Facebook or any social networking site.
Highly recommend you check this guide out and send it to your friends and family. Get it from his blog here:
http://spylogic.net/item/370
Highly recommend you check this guide out and send it to your friends and family. Get it from his blog here:
http://spylogic.net/item/370
December 27, 2008
New electronic Christmas gifts may have a special 'present'

As I celebrate this holiday season with my family and friends I'm finding myself busier than ever with security work - and it's not dealing with any infected PCs of my family and friends. You see, this year we have received more electronic devices that can plug into a computer than ever.

What's the big deal you ask? Concerns about malware-infected devices and their software.
Malware-infected devices isn't a new issue: we've had reports of new devices being infected with malware for the past couple years. This year is no different: I know first hand of several such instances where MP3 players or digital video frames come out of the box with this additional 'special gift' that when plugged into a computer drops malicious code onto it used to join botnets, steal Internet website account credentials, or who knows what. Oh, and it's not just the devices themselves, the software that comes with the hardware has had issues. Stories: Best Buy sold infected digital picture frames (Jan 2008) and here, Vuescape frames have infected software (Aug 2008), Samsung ships infected picture frame software CD (Dec 2008).
So while the percentage of these infected devices is still very low I'm still taking the precaution and plugging these things into my security test lab of 'victim' machines and will monitor what they do. Even if you don't have a lab like mine you can still exercise caution when hooking these up to your system. You can run system monitoring tools such as Process Monitor or Process Explorer from the brilliant folks in the Microsoft SysInternals team or a packet sniffer like Wireshark. You might also run something that monitors network connections, such as Windows built in utility NETSTAT (sorry, I don't know a Mac equivalent), while you plug the device in or install the software to see whether your machine visits a site on the Internet during the install and usage of the device and it's bundled software.
I'm raising an eggnog toast to all of us receiving electronic gifts without the special additional 'gift'. Hope your holiday is a malware-free one.
December 24, 2008
CastleCops has closed - this is a sad day

I've just learned that one of the great security communities has closed its doors: CastleCops has pulled the plug as of December 23 this year. The great folks volunteering their time there did some great work in fighting the good fight taking on the criminals and other miscreants on the Internet.
It was founded by Paul and Robin Laudanski many years ago (I don't know exactly when) and over those years they have spent countless hours building and supporting that community. They showed all of what can be done when we band together to fight the good fight.
A big THANK YOU goes out to Paul, Robin, everyone else at CastleCops for everything this did! This community will be missed.
December 21, 2008
White powder letters sent to state governors: dry run or distraction?
The Dallas office of the FBI reports that letters with a suspicious white powder has been sent to the offices of 40 United States state governors as well several overseas US Embassies. Initial field tests indicate no biological agent is present in the white powder so at least we know it's not anthrax used in the attacks against media outlets and the US Congress.
My question is: dry run, distraction, or neither? Was this a dry run preparing for a forthcoming attack? Maybe the purpose is to distract and pull government resources toward this ruse to allow for other nefarious work to occur undetected? Or neither, maybe someone looking for 15 minutes of fame?
For the security and IT professionals out there hopefully this incident reminds you to always look for the motive(s), think about your detection systems, and how you handle post-incident followups.
Motives of Your Attackers
 You might consider conducting a review of possible motives of your attackers, consider the scenarious and outcomes, and then determine if your countermeasures are sufficient. If you have a team (IOW there's more than 1 of you) this would be a good candidate for a brainstorming session in a conference room or maybe at offsite location. Oh, and let's not forget about determining what information (re intelligence) your attacker can obtain about your organization without actually atacking, this should be part of any counterintelligence program.
 Detection Capabilities
Are you able to detect attack dry runs or rehearsals against your computing and physical systems? Can you detect your adversary profiling your systems? Consider how they would perform this activity and compare it against your detection systems in place, I guarantee you'll find gaps that will cause you to consider additional options.
Incident Followups
One such followup might be to increase monitoring of your systems across the board, not just the systems involved. As mentioned earlier you might also consider your counterintelligence program (or build one if you dont have one already). Also, as part of the incident investigation process you should be to look at any strange or abnormal behaviour of related systems leading up to or around the time of the incident under investigation. This is a normal practice in physical security incidents but sometimes is forgotten during computer-related incidents.
Let's hope that there are no future real attacks relating to this latest incident and that the good people at the FBI find the culprit of this latest scare.
As for your environment, take a moment or two (or three) and consider your capabilities and where to improve them.
December 14, 2008
Rogue security software screenshot collection
The look of rogue/fraudulent security software has evolved to where it's impossible to distinguish between them and the legitimate applications.


Want to see how close - see Sunbelt Software Patrick Jordon's screenshot collection here.


Want to see how close - see Sunbelt Software Patrick Jordon's screenshot collection here.
December 3, 2008
Let me Google that for you
Now I've seen everything: there's a website that will do a Google search for you by showing you how to use Google. Huh? The creators say they created it as a way to help the search-engine challenged Internet users that ask you questions they could find the answers to on Google. Quote on their website: "This is for all those people that find it more convenient to bother you with their question rather than google it for themselves."
Screenshot of their website:
 Here's how it works:
1. Visit the site http://letmegooglethatforyou.com
2. Enter your search criteria in the box and press the Google Search button
3. It will create a link for you that you can copy and send to that search-engine challenged person you know. Example: http://letmegooglethatforyou.com/?q=screensavers
4. When they click the link they'll see an animated cursor showing them how to submit a Google search and then actually runs the search on Google redirecting them to Google's website for results.
So, the paranoid side of me wonders if these guys are going to track the searches and then sell the data to advertisers. Also, they have Google's graphic/logo on their page...wonder how long until Google tells them to remove it. Then again, why would they? They are generating search traffic for them. ;-)
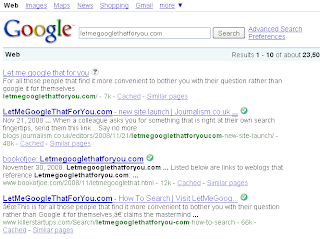
Ha, here's some irony: the site is indexed on Google.com.
Check it out for yourself:
http://letmegooglethatforyou.com or http://lmgtfy.com
Screenshot of their website:
 Here's how it works:
1. Visit the site http://letmegooglethatforyou.com
2. Enter your search criteria in the box and press the Google Search button
3. It will create a link for you that you can copy and send to that search-engine challenged person you know. Example: http://letmegooglethatforyou.com/?q=screensavers
4. When they click the link they'll see an animated cursor showing them how to submit a Google search and then actually runs the search on Google redirecting them to Google's website for results.
So, the paranoid side of me wonders if these guys are going to track the searches and then sell the data to advertisers. Also, they have Google's graphic/logo on their page...wonder how long until Google tells them to remove it. Then again, why would they? They are generating search traffic for them. ;-)

Ha, here's some irony: the site is indexed on Google.com.
Check it out for yourself:
http://letmegooglethatforyou.com or http://lmgtfy.com
Subscribe to:
Posts (Atom)


